零基础保姆级小白节点搭建教学,目前最安全最稳定的搭建方式,通过x-ui面板实现单端口多用户合租
January 14, 2023March 10, 2023
VPS购买
搬瓦工:https://bwg.bulianglin.com
优惠码: BWHNCXNVXV
执行**unminimize之后,中途如果出现如下图的A new version提示信息,输入数字2**,再回车即可
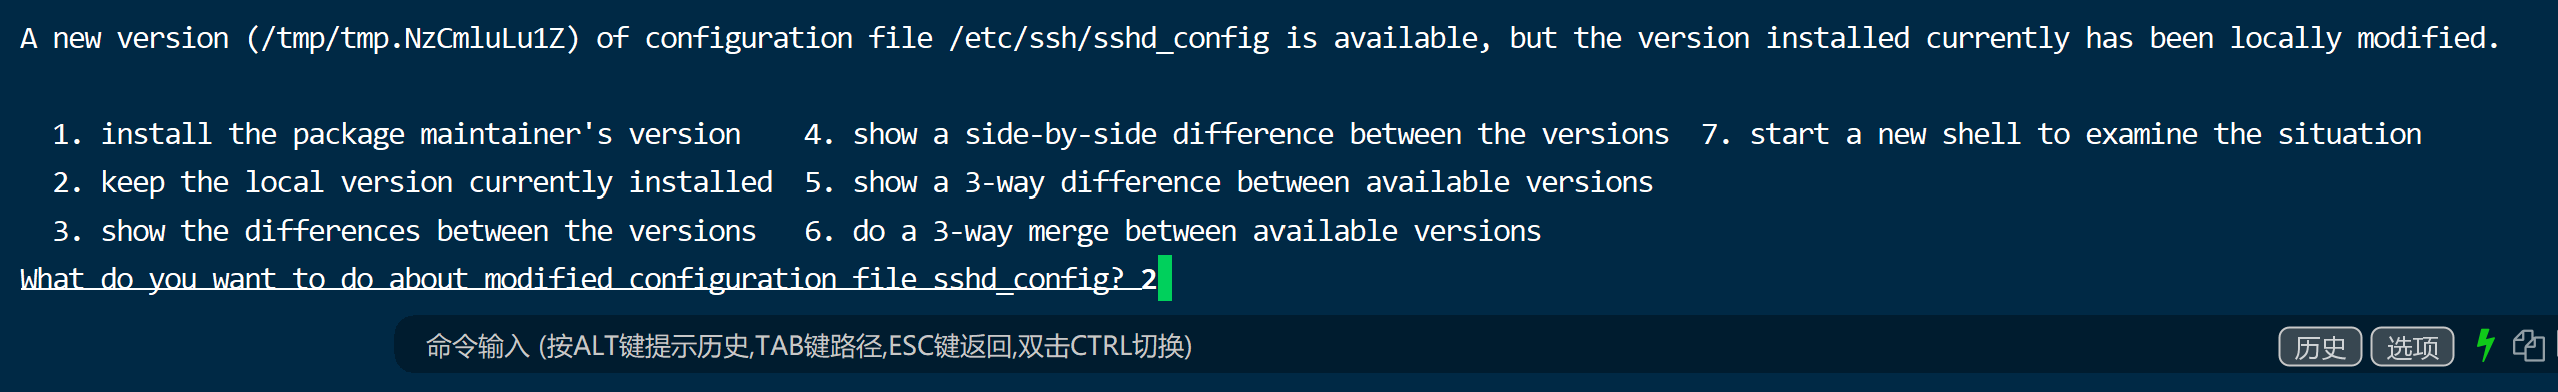
输入数字2,再回车
域名购买
namesilo:https://name.bulianglin.com
优惠码:oldtong
SSH工具
FinalShell:https://www.hostbuf.com/t/988.html
节点搭建
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
| #更新软件源
apt update
#启用 BBR TCP 拥塞控制算法
echo "net.core.default_qdisc=fq" >> /etc/sysctl.conf
echo "net.ipv4.tcp_congestion_control=bbr" >> /etc/sysctl.conf
sysctl -p
#安装x-ui:
bash <(curl -Ls https://raw.githubusercontent.com/vaxilu/x-ui/master/install.sh)
#安装nginx
apt install nginx
#安装acme:
curl https://get.acme.sh | sh
#添加软链接:
ln -s /root/.acme.sh/acme.sh /usr/local/bin/acme.sh
#切换CA机构:
acme.sh --set-default-ca --server letsencrypt
#申请证书:
acme.sh --issue -d 你的域名 -k ec-256 --webroot /var/www/html
#安装证书:
acme.sh --install-cert -d 你的域名 --ecc --key-file /etc/x-ui/server.key --fullchain-file /etc/x-ui/server.crt --reloadcmd "systemctl force-reload nginx"
|
寻找适合的伪装站
http站点优先,个人网盘符合单节点大流量特征
示例关键字:intext:登录 Cloudreve
配置nginx
配置文件路径:/etc/nginx/nginx.conf
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
| user www-data;
worker_processes auto;
pid /run/nginx.pid;
include /etc/nginx/modules-enabled/*.conf;
events {
worker_connections 1024;
}
http {
sendfile on;
tcp_nopush on;
tcp_nodelay on;
keepalive_timeout 65;
types_hash_max_size 2048;
include /etc/nginx/mime.types;
default_type application/octet-stream;
gzip on;
server {
listen 443 ssl;
server_name nicename.co; #你的域名
ssl_certificate /etc/x-ui/server.crt; #证书位置
ssl_certificate_key /etc/x-ui/server.key; #私钥位置
ssl_session_timeout 1d;
ssl_session_cache shared:MozSSL:10m;
ssl_session_tickets off;
ssl_protocols TLSv1.2 TLSv1.3;
ssl_prefer_server_ciphers off;
location / {
proxy_pass https://bing.com; #伪装网址
proxy_redirect off;
proxy_ssl_server_name on;
sub_filter_once off;
sub_filter "bing.com" $server_name;
proxy_set_header Host "bing.com";
proxy_set_header Referer $http_referer;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header User-Agent $http_user_agent;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
proxy_set_header X-Forwarded-Proto https;
proxy_set_header Accept-Encoding "";
proxy_set_header Accept-Language "zh-CN";
}
location /ray { #分流路径
proxy_redirect off;
proxy_pass http://127.0.0.1:10000; #Xray端口
proxy_http_version 1.1;
proxy_set_header Upgrade $http_upgrade;
proxy_set_header Connection "upgrade";
proxy_set_header Host $host;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
}
location /xui { #xui路径
proxy_redirect off;
proxy_pass http://127.0.0.1:9999; #xui监听端口
proxy_http_version 1.1;
proxy_set_header Host $host;
}
}
server {
listen 80;
location /.well-known/ {
root /var/www/html;
}
location / {
rewrite ^(.*)$ https://$host$1 permanent;
}
}
}
|
每次修改nginx配置文件后必须使用 systemctl reload nginx 命令重新加载配置文件
多用户合租
通过修改nginx的配置文件实现ws path路径分流
1
2
3
4
5
6
7
8
9
10
| location /ray { #分流路径
proxy_redirect off;
proxy_pass http://127.0.0.1:10000; #Xray端口
proxy_http_version 1.1;
proxy_set_header Upgrade $http_upgrade;
proxy_set_header Connection "upgrade";
proxy_set_header Host $host;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
}
|
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
| location /shop {
proxy_http_version 1.1;
proxy_set_header Upgrade $http_upgrade;
proxy_set_header Connection "upgrade";
proxy_pass_header Set-Cookie;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header X-Forwarded-For $remote_addr;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
proxy_set_header Host $host;
proxy_redirect off;
add_header Access-Control-Allow-Origin *;
add_header Access-Control-Allow-Methods "POST, GET,PUT,DELETE, OPTIONS";
add_header Access-Control-Allow-Headers "Origin, Authorization, Accept";
add_header Access-Control-Allow-Credentials true;
proxy_pass http://localhost:8092/;
}
|
1
2
3
4
5
6
7
8
9
10
11
12
13
| #安装证书工具:
curl https://get.acme.sh | sh; apt install socat -y || yum install socat -y; ~/.acme.sh/acme.sh --set-default-ca --server letsencrypt
#三种方式任选其中一种,申请失败则更换方式
#申请证书方式1:
~/.acme.sh/acme.sh --issue -d 你的域名 --standalone -k ec-256 --force --insecure
#申请证书方式2:
~/.acme.sh/acme.sh --register-account -m "${RANDOM}@chacuo.net" --server buypass --force --insecure && ~/.acme.sh/acme.sh --issue -d 你的域名 --standalone -k ec-256 --force --insecure --server buypass
#申请证书方式3:
~/.acme.sh/acme.sh --register-account -m "${RANDOM}@chacuo.net" --server zerossl --force --insecure && ~/.acme.sh/acme.sh --issue -d 你的域名 --standalone -k ec-256 --force --insecure --server zerossl
#安装证书:
~/.acme.sh/acme.sh --install-cert -d 你的域名 --ecc --key-file /etc/x-ui/server.key --fullchain-file /etc/x-ui/server.crt
|
管理acme证书
安装 acme.sh
1
| curl https://get.acme.sh | sh
|
安装完毕后可以使用 acme.sh --version 检查状态
1
2
3
| # acme.sh --version
https://github.com/acmesh-official/acme.sh
v3.0.1
|
如果需要升级 acme.sh 则运行
1
2
3
4
5
6
7
8
| # 升级到最新版
acme.sh --upgrade
# 开启自动升级
acme.sh --upgrade --auto-upgrade
# 关闭自动升级
acme.sh --upgrade --auto-upgrade 0
|
生成证书
HTTP 认证方式
1
| acme.sh --issue -d example.com -d www.example.com --webroot /home/wwwroot/example.com/
|
DNS 认证方式
各大 dns 提供商的使用方式参考此处
此处以 cloudflare 为例:
1
2
3
4
5
| export CF_Token="sdfsdfsdfljlbjkljlkjsdfoiwje"
export CF_Account_ID="xxxxxxxxxx"
export CF_Zone_ID="xxxxxxxxxx"
acme.sh --issue --dns dns_cf -d example.com -d *.example.com --server letsencrypt
|
操作已安装证书
1
2
3
4
5
| # 查看已安装证书
acme.sh --list
# 删除证书
acme.sh remove <SAN_domains>
|
安装证书
1
2
3
4
5
| # 以 example.com 为例
acme.sh --installcert -d example.com \
--key-file /usr/local/nginx/ssl/example.com.key \
--fullchain-file /usr/local/nginx/ssl/fullchain.cer \
--reloadcmd "systemctl reload nginx ; systemctl restart v2ray"
|
更新证书
如果需要手动续签,则执行
1
| acme.sh --renew -d example.com --force
|





