mkdir /application tar xf openvpn-2.2.2.tar.gz -C /application/ cd /application/openvpn-2.2.2/ ./configure --with-lzo-lib=/usr/local/lib--with-lzo-headers=/usr/local/include make make install
检查安装结果
1
2
[root@vpnserver openvpn-2.2.2]# which openvpn
/usr/local/sbin/openvpn
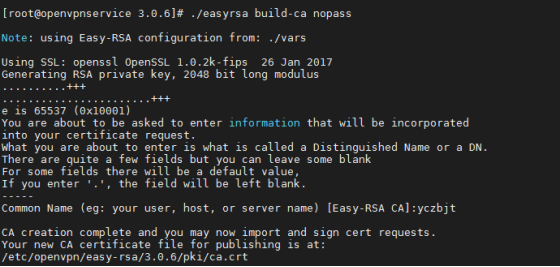
[root@vpnserver 2.0]# ./build-ca
Generating a 1024 bit RSA private key
...++++++
......................................++++++
writing new private key to 'ca.key'
-----
You are about to be asked to enter information that will beincorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Nameor a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [CN]:
State or Province Name (full name) [HB]:
Locality Name (eg, city) [WuHan]:
Organization Name (eg, company) [sunny]:
Organizational Unit Name (eg, section) [sunny]:
Common Name (eg, your name or your server's hostname) [sunny]:
Name [sunny]:
Email Address [519209@qq.com]:
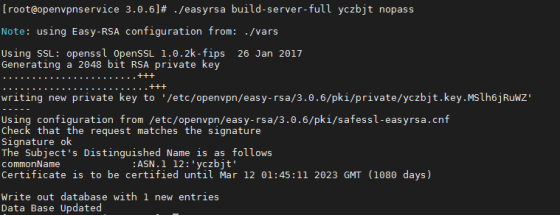
[root@vpnserver 2.0]# ./build-key-server server
Generating a 1024 bit RSA private key
....................++++++
............................................++++++
writing new private key to 'server.key'
-----
You are about to be asked to enter information that will beincorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Nameor a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [CN]:
State or Province Name (full name) [HB]:
Locality Name (eg, city) [WuHan]:
Organization Name (eg, company) [sunny]:
Organizational Unit Name (eg, section) [sunny]:
Common Name (eg, your name or your server's hostname) [server]:
Name [sunny]:
Email Address [519209@qq.com]:
Please enter the following 'extra' attributes
to be sent with your certificate request
A challenge password []:123456
An optional company name []:sunny
Using configuration from/application/openvpn-2.2.2/easy-rsa/2.0/openssl-1.0.0.cnf
Check that the request matches the signature
Signature ok
The Subject's Distinguished Name is as follows
countryName          :PRINTABLE:'CN'
stateOrProvinceName  :PRINTABLE:'HB'
localityName         :PRINTABLE:'WuHan'
organizationName     :PRINTABLE:'sunny'
organizationalUnitName:PRINTABLE:'sunny'
commonName            :PRINTABLE:'server'
name                 :PRINTABLE:'sunny'
emailAddress         :IA5STRING:'519209@qq.com'
Certificate is to be certified until Jul  5 09:04:46 2026 GMT (3650 days)
Sign the certificate? [y/n]:y
1 out of 1 certificate requests certified, commit? [y/n]y
Write out database with 1 new entries
Data Base Updated
[root@vpnserver 2.0]# ./build-key test
Generating a 1024 bit RSA private key
.....................................++++++
..++++++
writing new private key to 'test.key'
-----
You are about to be asked to enter information that will beincorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Nameor a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [CN]:
State or Province Name (full name) [HB]:
Locality Name (eg, city) [WuHan]:
Organization Name (eg, company) [sunny]:
Organizational Unit Name (eg, section) [sunny]:
Common Name (eg, your name or your server's hostname) [test]:
Name [sunny]:
Email Address [519209@qq.com]:
Please enter the following 'extra' attributes
to be sent with your certificate request
A challenge password []:123456
An optional company name []:sunny
Using configuration from/application/openvpn-2.2.2/easy-rsa/2.0/openssl-1.0.0.cnf
Check that the request matches the signature
Signature ok
The Subject's Distinguished Name is as follows
countryName          :PRINTABLE:'CN'
stateOrProvinceName  :PRINTABLE:'HB'
localityName         :PRINTABLE:'WuHan'
organizationName     :PRINTABLE:'sunny'
organizationalUnitName:PRINTABLE:'sunny'
commonName           :PRINTABLE:'test'
name                 :PRINTABLE:'sunny'
emailAddress         :IA5STRING:'519209@qq.com'
Certificate is to be certified until Jul  5 09:13:01 2026 GMT (3650 days)
Sign the certificate? [y/n]:y
1 out of 1 certificate requests certified, commit? [y/n]y
Write out database with 1 new entries
Data Base Updated
[root@vpnserver 2.0]# ./build-key-pass sunny
Generating a 1024 bit RSA private key
...++++++
...............................................++++++
writing new private key to 'sunny.key'
Enter PEM pass phrase:                         #此处需要输入用户密码
Verifying - Enter PEM pass phrase:     #此处需要确认用户密码
-----
You are about to be asked to enter information that will beincorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Nameor a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [CN]:
State or Province Name (full name) [HB]:
Locality Name (eg, city) [WuHan]:
Organization Name (eg, company) [sunny]:
Organizational Unit Name (eg, section) [sunny]:
Common Name (eg, your name or your server's hostname) [sunny]:
Name [sunny]:
Email Address [519209@qq.com]:

Please enter the following 'extra' attributes
to be sent with your certificate request
A challenge password []:123456
An optional company name []:sunny
Using configuration from/application/openvpn-2.2.2/easy-rsa/2.0/openssl-1.0.0.cnf
Check that the request matches the signature
Signature ok
The Subject's Distinguished Name is as follows
countryName          :PRINTABLE:'CN'
stateOrProvinceName  :PRINTABLE:'HB'
localityName         :PRINTABLE:'WuHan'
organizationName      :PRINTABLE:'sunny'
organizationalUnitName:PRINTABLE:'sunny'
commonName           :PRINTABLE:'sunny'
name                 :PRINTABLE:'sunny'
emailAddress         :IA5STRING:'519209@qq.com'
Certificate is to be certified until Jul  5 09:16:29 2026 GMT (3650 days)
Sign the certificate? [y/n]:
1 out of 1 certificate requests certified, commit? [y/n]y
Write out database with 1 new entries
Data Base Updated
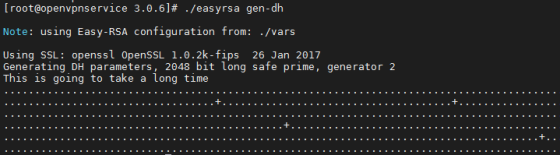
[root@vpnserver 2.0]# ./build-dh
Generating DH parameters, 1024 bit long safe prime, generator 2
This is going to take a long time
.........................................+.............................++*++*++*
[root@vpnserver 2.0]# ls keys/dh1024.pem
keys/dh1024.pem
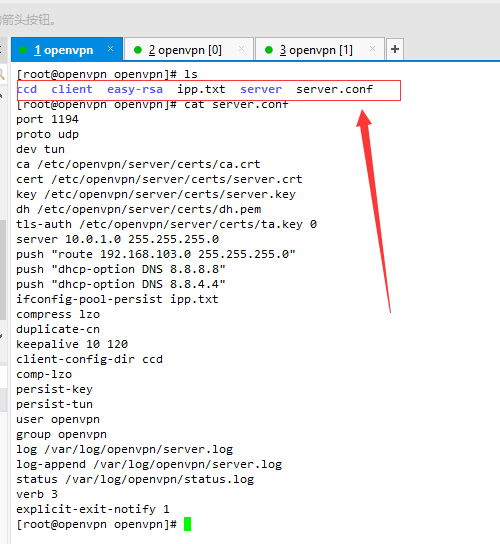
local 192.168.3.201
port 52115
proto tcp
dev tun
ca /etc/openvpn/keys/ca.crt
cert /etc/openvpn/keys/server.crt
key /etc/openvpn/keys/server.key
dh /etc/openvpn/keys/dh1024.pem
server 10.8.0.0 255.255.255.0
push "route 192.168.18.0 255.255.255.0"
ifconfig-pool-persist ipp.txt
keepalive 10 120
comp-lzo
persist-key
persist-tun
status openvpn-status.log
log /var/log/openvpn.log
duplicate-cn
client-to-client
verb 3
[root@vpnserver openvpn]# less /var/log/openvpn.log
Options error: You must define private key file (--key) or PKCS#12file (--pkcs12)
Use --help for more information.
client
dev tun
proto tcp
remote 192.168.3.201 52115
resolv-retry infinite
nobind
persist-key
persist-tun
ca ca.crt
cert test.crt
key test.key
ns-cert-type server
comp-lzo
verb 3
#!/bin/sh
###########################################################
# checkpsw.sh (C) 2004 Mathias Sundman <mathias@openvpn.se>
#
# This script will authenticate OpenVPN users against
# a plain text file. The passfile should simply contain
# one row per user with the username first followed by
# one or more space(s) or tab(s) and then the password.
PASSFILE="/etc/openvpn/psw-file"
LOG_FILE="/var/log/openvpn-password.log"
TIME_STAMP=`date "+%Y-%m-%d %T"`
###########################################################
if [ ! -r "${PASSFILE}" ]; then
echo "${TIME_STAMP}: Could not open password file\"${PASSFILE}\" for reading." >> ${LOG_FILE}
exit 1
fi
CORRECT_PASSWORD=`awk'!/^;/&&!/^#/&&$1=="'${username}'"{print $2;exit}'${PASSFILE}`
if [ "${CORRECT_PASSWORD}" = "" ]; then
echo "${TIME_STAMP}: User does not exist: username=\"${username}\",password=\"${password}\"." >> ${LOG_FILE}
exit 1
fi
if [ "${password}" = "${CORRECT_PASSWORD}" ]; then
echo "${TIME_STAMP}: Successful authentication:username=\"${username}\"." >> ${LOG_FILE}
exit 0
fi
echo "${TIME_STAMP}: Incorrect password:username=\"${username}\", password=\"${password}\".">> ${LOG_FILE}
exit 1</mathias@openvpn.se>
client
dev tun
proto tcp
remote 192.168.3.201 52115
resolv-retry infinite
nobind
persist-key
persist-tun
ca ca.crt
;cert test.crt
;key test.key
ns-cert-type server
comp-lzo
verb 3
auth-user-pass